WordPress sites
Install WordPress, keep a whole estate of sites updated by policy with automatic rollback, sign in to wp-admin in one click, manage the site's users, match plugins against a vulnerability feed and harden each site.
Sites created with the WordPress runtime get a WordPress tab, and the WordPress tab of Infrastructure > Websites (beside All websites) lists every managed WordPress site together as an estate. Tenvara checks what each site runs every night, updates it by policy, flags vulnerable plugins and drifting hardening, and signs you in to wp-admin without a password.
Installing WordPress
Creating a site with the WordPress runtime installs WordPress for you (see Creating and managing sites). To install it on an existing WordPress-runtime site that does not have it yet:
- Open the site's WordPress tab and choose Install WordPress.
- Enter the Site title, Admin user (not admin, administrator or root) and Admin email.
- Confirm Install. Anything already in the site is replaced.
WordPress, its database and user, and an administrator account are created. Tenvara checks that the generated password really signs in before it keeps it, and shows it once; after that it is kept encrypted and can be revealed under Admin sign-in.
The WordPress estate
Open Infrastructure > Websites and its WordPress tab. It lists every managed WordPress site with its customer and server, its WordPress version (and whether a newer one is out), the updates waiting or due, known vulnerabilities with the worst score, core checksums, hardening, and whether the site is paused or has its own policy. Filter by customer, policy and state.
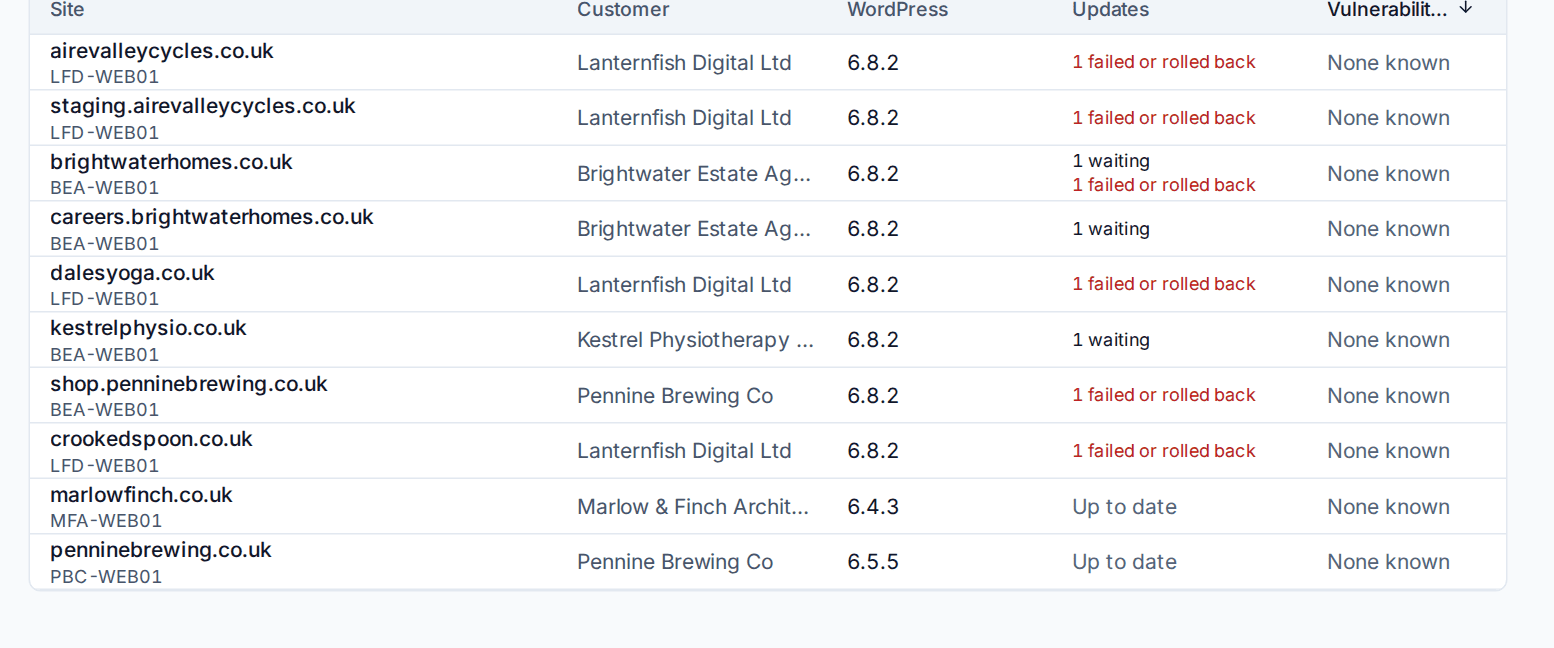
Every night each site's WordPress core, plugins, themes, administrators and core checksums are read again, and its hardening is checked, so the list is never more than a day old. Check now on a site's tab reads it at once.
Automatic updates
Updates follow a policy. The Estate policy (the button on the WordPress tab, or WordPress in Settings > Infrastructure) applies to every site, a customer can have its own, and a site keeps only what it changes.
| Setting | Choices |
|---|---|
| Minor WordPress releases | At once, or in the window |
| Major releases, plugins and themes | Automatically in the window after a delay (3 days by default), or by hand |
| The window | A time range in your time zone, for example 02:00 to 05:00 (it may run past midnight) |
| Exclusions | Plugins or themes never updated automatically |
| Pause | Stops automatic updates for the site |
An update that fixes a known vulnerability skips the delay and the window.
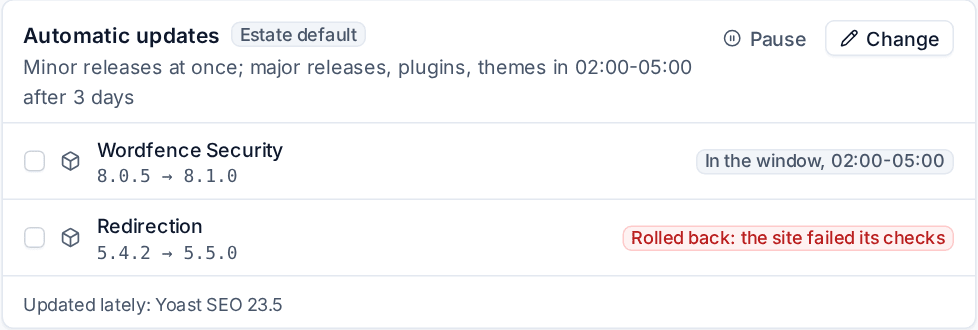
On a site's WordPress tab, Automatic updates shows the policy in words, what is waiting and why (for example In the window, 02:00-05:00), what was updated lately, and anything that failed. Pause and Change set the site's own policy, and ticking waiting updates then Update now runs them whatever the policy says.
Updates are guarded
Before updating, the server snapshots the site and its database and checks that / and /wp-login.php answer. After updating it checks them again, and if they stop answering it rolls everything back by itself. A rolled back update shows as Rolled back: the site failed its checks and is not tried again by itself.
You can also update by hand at any time: Update all, or Update on one row in Plugins or Themes, or WordPress core on its own.
Known vulnerabilities
Tenvara matches every site's plugins, themes and WordPress version against the Wordfence Intelligence vulnerability feed. Connect it with your own Wordfence Intelligence API key (free with a Wordfence account) in Settings > Infrastructure; the feed is then read every night. Until a key is added, the WordPress tab says that vulnerabilities are not being matched. Each site's Known vulnerabilities lists what affects it, and each vulnerable plugin, theme or core raises an alert (critical for the most serious scores).
Admin sign-in
Admin sign-in shows the administrator account Tenvara holds for the site, and whether its password still signs in (checked every night).
- Open wp-admin signs you straight in with a single-use link that expires within a minute. Nothing is typed and no password is shown.
- Reset password makes a new password on the server, checks it signs in, and shows it once.
- Plain wp-admin address is the normal sign-in page, for when you want to use the password.
If someone changes that administrator's password in WordPress, the card says The stored password no longer matches, a warning alert opens, and Reset password puts it right.
Users
The Users section lists the site's users (administrators and editors first) with their role, email, last sign-in, when their password last changed and whether they have two-factor sign-in. Use Refresh to read them again and Add user to add one with a generated or typed password, optionally sending WordPress's welcome email.
From a user's menu you can reset their password (generated and shown once, typed, or WordPress's own reset email), change their role, remove them (their content goes to a user you choose; the last administrator cannot be removed), and Sign in as this user (administrators only, with a single-use link).
Tenvara flags common risks: more administrators than you allow (1 by default), a user called "admin", administrators who have not signed in for 90 days, administrators without a second factor when a two-factor plugin is installed, and passwords still stored under an old hash. Change the limits under WordPress in Settings > Infrastructure, per customer if needed.
Note: Every sign-in, reset and user change is recorded in the site's Operations and the audit log, with no password in either.
Hardening
Hardening checks eight measures, including that file editing in the dashboard and debug output are off, the dashboard is only served over HTTPS, unique keys and salts are set, no user is called "admin", wp-config.php is not readable by other users, xmlrpc.php is blocked, and no inactive plugins are left installed. Press Apply to put the missing ones in place. A measure that stops passing later raises an alert.
Core checksums confirm WordPress's core files match the official release. A mismatch raises a critical alert, as it can mean files were tampered with.
Alerts for WordPress sites
WordPress sites share the web server alerts (site not answering, certificate expiry, failed backups and failed operations), plus: a vulnerable plugin, theme or core, WordPress core behind for 14 days, core checksums that do not match, a hardening check that no longer passes, an update rolled back, and a stored administrator password that no longer works. See Certificates, operations and alerts.
Was this page helpful?
Thanks for the feedback.